
NIS2 compliance software that works with you — local, no cloud.
From scoping check to reporting duty: the NIS2-Manager is NIS2 and ISMS software that covers the Article 21 risk-management measures, runs locally on Windows and keeps your sensitive compliance data in-house.
Local · no cloud requirement · subscription from EUR 499 per year net · business (B2B)
Updated: 8 September 2026
What applies
The NIS2-Manager is built on VdS 10100, a German information security standard aligned with ISO/IEC 27001, and maps its measures to ISO/IEC 27001 controls. It is not a certification tool for ISO/IEC 27001.
Everything for NIS2 in one tool
One purchase, every building block of the duty of care — no per-module fee.
Processing and asset register
Measures and risk assessment
Report assistant 24h / 72h / 1 month
Reports as DOCX and PDF
What you actually get
Screenshots from the English edition with the EU country pack, filled with sample data.
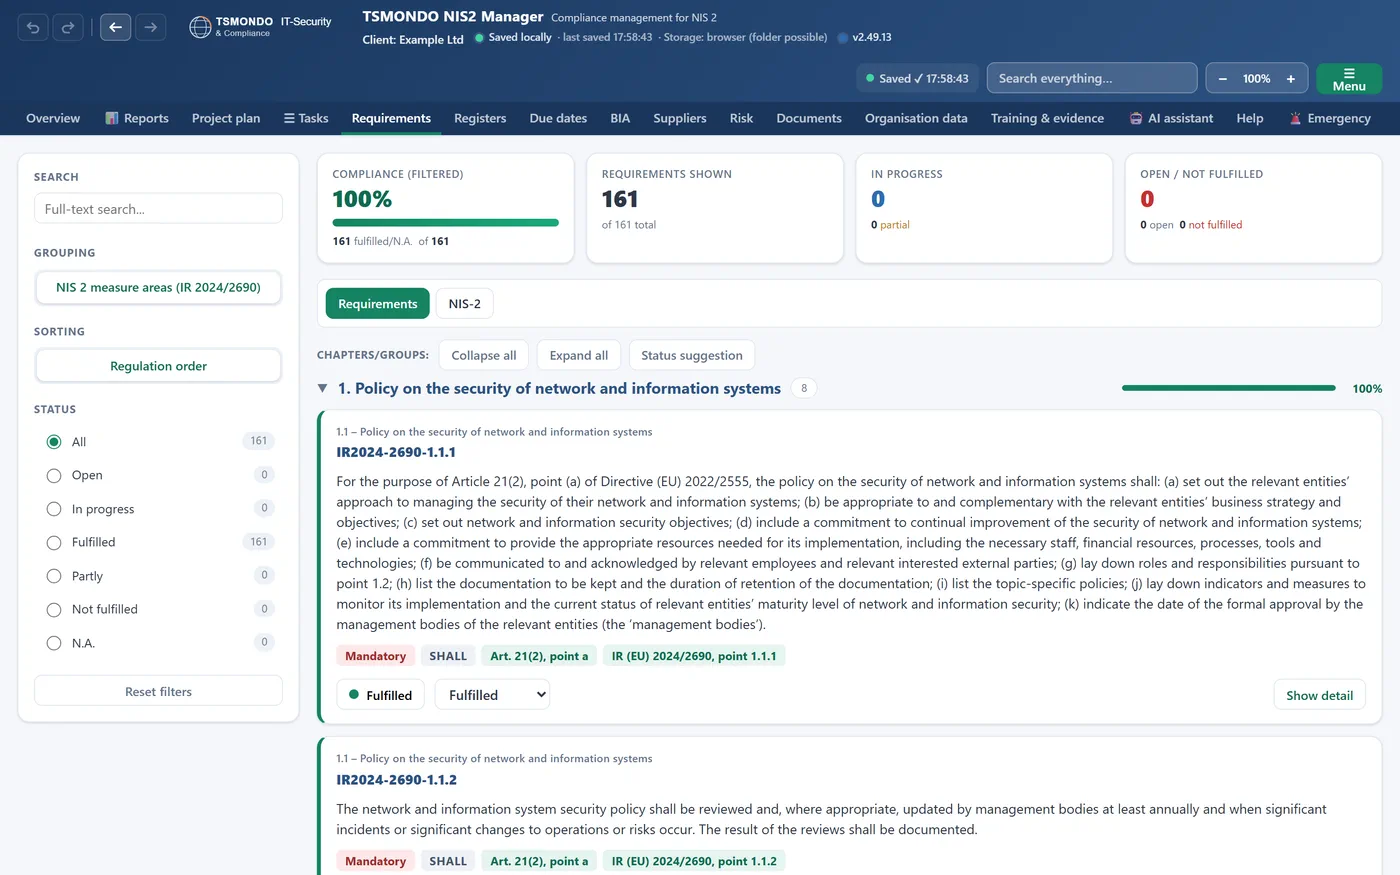
Filtered, not just listed
Every measure from the Implementing Regulation sits behind a filter for status and obligation level, so you work the mandatory ones first.
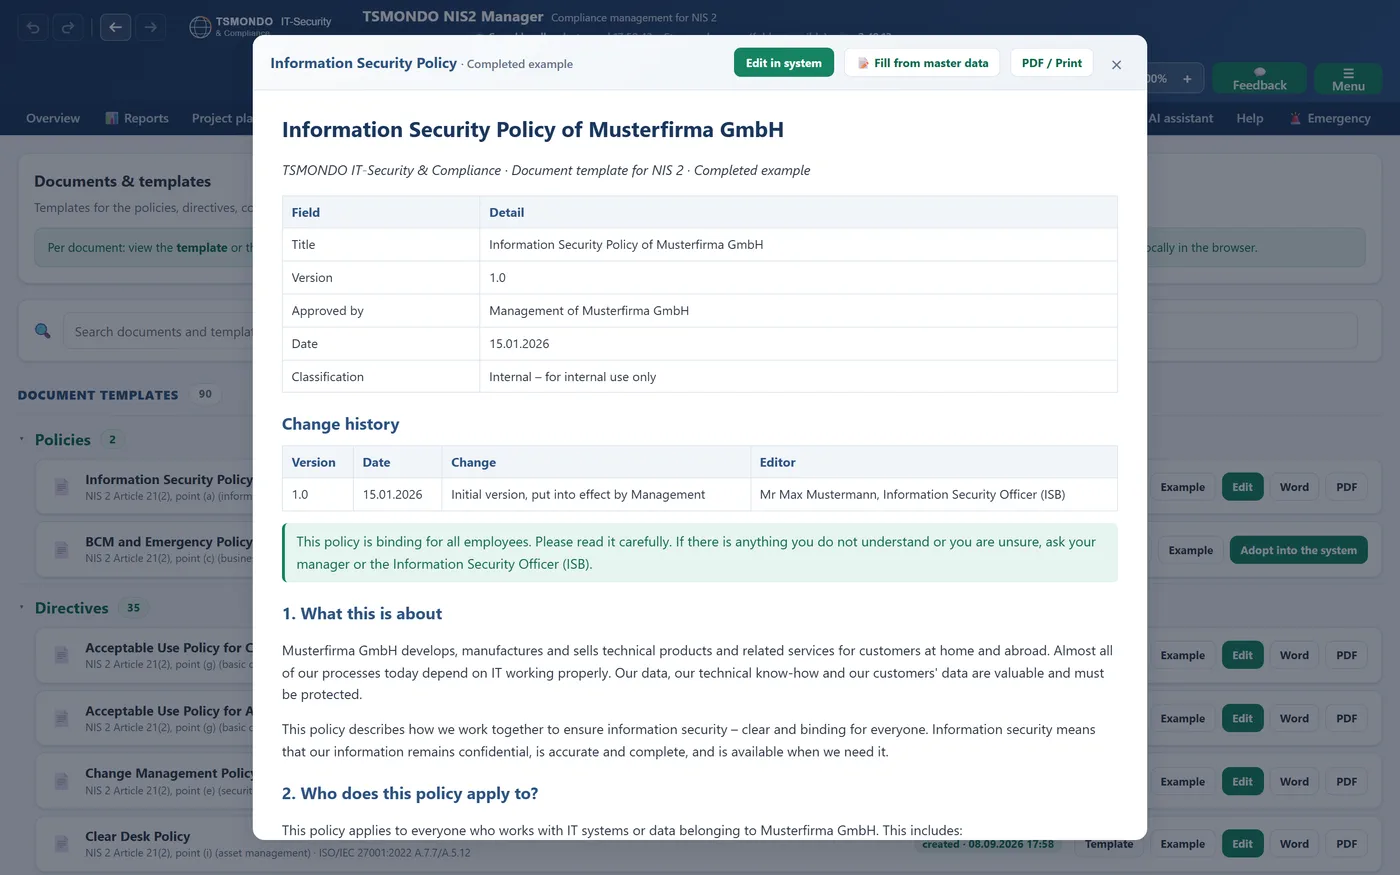
Documents, not blank pages
A completed example policy shows the structure, the change history and the wording you adapt, rather than a blank template to start from.
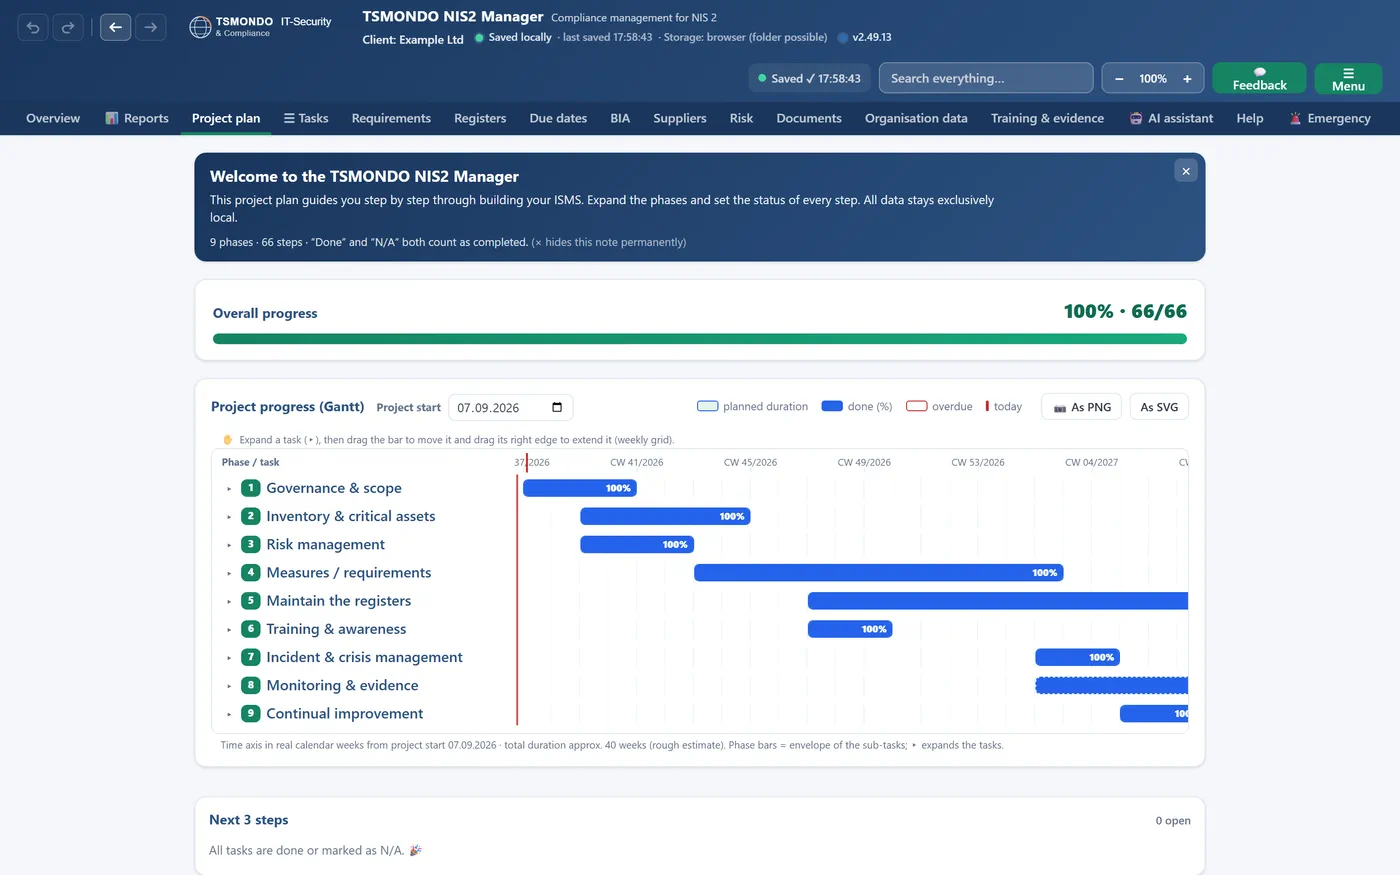
Plan, not a guess
Nine phases laid out against calendar weeks turn the duty of care into a schedule your team can actually follow.
Local instead of cloud — your data stays yours
Your register, measures and risk assessments hold the most sensitive security information in your organisation. That does not belong in a third-party cloud database.
- Runs locally on Windows, no cloud requirement and no data leaving your control
- Network-capable: several staff work together on the same records
- Local AI drafting help or optional Mistral EU — your choice
- Back-up and export in your own hands at any time
Not an empty framework, but a populated baseline
The NIS2-Manager ships with the full structure of the directive and ready-made templates, so you do not start from zero.
ISMS software, not a compliance checkbox
The TSMONDO NIS2 Manager does not tick one obligation off a list — it runs an information security management system. Requirements, risks, evidence, suppliers and documents live in a single data set, and that same data set answers NIS2, ISO/IEC 27001, ISO 22301 and Article 32 GDPR at the same time. You maintain one status and generate eleven reports from it, among them the statement of applicability, two standards conformity reports and the annual management review. If you start today because the law requires it, you already have the structure in place should certification follow. The application runs locally on your own machine, with no cloud and no server account.
- Compliance report — tells you in one figure how far you have come, and in one table which chapter is holding you back.
- ISO/IEC 27001 conformity report — shows how much of your NIS2 work already counts towards ISO/IEC 27001:2022; the status is derived from a curated mapping and is subject to expert review.
- ISO 22301 conformity report (BCM) — the same view for business continuity, with a gap list instead of a gut feeling, likewise subject to expert review.
- Statement of applicability (SoA) — answers, for every requirement, whether it applies to you, how far it is implemented and which document proves it.
- GDPR Art. 32 — technical and organisational measures conformity report — gives you the answer a supervisory authority asks for: which measures are actually in place.
- Management review (combined annual review) — replaces the slide deck that otherwise gets assembled by hand once a year.
- Documentation evidence per obligation — shows you before the audit where a piece of evidence is missing, rather than during it.
- Emergency plan — puts reporting deadlines, contacts and recovery order on a single sheet for the day it matters.
- Supplier report — turns a supplier self-assessment into a traceable score with history; it does not replace a full supplier audit.
- Project progress report (ISMS implementation) — answers the board's question about when you will be finished, in phases rather than in optimism.
- Management report — condenses completion rate, residual risks, deadlines and open actions into the pages leadership actually reads.
What the statement of applicability does
The statement of applicability is the list that records, for every single requirement, whether it applies to you, how far it is implemented and why — it is the document that lets an auditor grasp the full scope of your management system in a few pages, and the one you would otherwise have to assemble by hand from spreadsheets.
From a specialist, built on the official texts
Not a resold platform, but the practice of a single expert — with the credentials that go with it and a basis in the source text itself.
One point of contact with the right qualifications
- ISO 27001 Lead Auditor and Lead Implementer
- ISACA CISM (Certified Information Security Manager)
- Certified data protection officer and IT security officer (TÜV)
- Member of the Alliance for Cyber Security (BSI, Germany)
On the source, not on a summary
- Built on Implementing Regulation (EU) 2024/2690
- Aligned with the ENISA Technical Implementation Guidance
- The 161 requirements come from the Annex of Implementing Regulation (EU) 2024/2690 itself
Organisations in industry, media, healthcare, the public sector and digital platforms work with TSMONDO — on security, NIS2 and data protection.


Data protection · datenschutzeinfach.com


Named with permission. Full list at tsmondo.de/referenzen and datenschutzeinfach.com/referenzen.
The NIS2 Manager, step by step
From the cockpit to the supplier questionnaire: a guided tour of every function. Watch the narrated video, browse online, read the PDF or download the PowerPoint for your team.
Narrated walkthrough, 10 minutes
Or browse slide by slide
Use the arrow keys once the viewer has focus. On a phone, swipe.
One licence per company, staggered by size
The price is set by the number of employees at the licensed company — across every site, with unlimited users throughout your company and no extra charge per seat. A German GmbH & Co. KG counts as one company; subsidiaries and sister companies within a group each need their own licence. All prices are net, plus VAT where applicable; the reverse charge procedure applies for businesses in other EU member states with a valid VAT identification number.
Launch offer until : 20% off the first year (annual plan) or the first three months (monthly plan). Enter code START20 at checkout — or apply the offer for an automatic discount.
Band 1 · up to 49 employees
EUR 49 net per month · or EUR 499 net per year
- One licence for your whole company, every site, unlimited users
- All program versions released during the term included
- Annual plan: renews for twelve months, cancellable in text form with one month's notice to the end of the term
- Monthly plan: renews every month, cancellable with effect from the end of the current month
Band 2 · 50-249 employees
EUR 99 net per month · or EUR 999 net per year
- One licence for your whole company, every site, unlimited users
- All program versions released during the term included
- Annual plan: renews for twelve months, cancellable in text form with one month's notice to the end of the term
- Monthly plan: renews every month, cancellable with effect from the end of the current month
Band 3 · 250-999 employees
EUR 199 net per month · or EUR 1,990 net per year
- One licence for your whole company, every site, unlimited users
- All program versions released during the term included
- Annual plan: renews for twelve months, cancellable in text form with one month's notice to the end of the term
- Monthly plan: renews every month, cancellable with effect from the end of the current month
Band 4 · 1,000-4,999 employees
EUR 299 net per month · or EUR 2,990 net per year
- One licence for your whole company, every site, unlimited users
- All program versions released during the term included
- Annual plan: renews for twelve months, cancellable in text form with one month's notice to the end of the term
- Monthly plan: renews every month, cancellable with effect from the end of the current month
5,000 employees or more: a tailored quote after a short call.
Request a quoteRequest the free demo by email
A portable ZIP for Windows, English interface — no account, no installation, nothing sent to us beyond the email below. The current full version and your licence key arrive by email once you buy a licence above.
Enter your email address — the download link arrives right away, along with appointment booking and the next steps.
This offer is addressed exclusively to businesses; there is no right of withdrawal. Payment runs through Stripe (SEPA direct debit or card) and the invoice arrives by email. Our terms and conditions apply.
Short and concrete
Does the NIS2-Manager run locally or in the cloud?
Fully local on Windows. No cloud requirement, no data leaving your control.
Does the software cover the NIS2 duty of care?
Yes. The structure is built on Article 21 NIS2 and Implementing Regulation (EU) 2024/2690.
Does the report assistant support the incident notification?
Yes, with the 24-hour, 72-hour and one-month deadlines and the national reporting channels (CSIRT / authority).
What does it cost?
The price depends on the number of employees at the company: four bands at EUR 49, 99, 199 or 299 net per month, or EUR 499, 999, 1,990 or 2,990 net per year. From 5,000 employees, we provide a tailored quote.
What language is the software in?
The interface and all reports are in English (current release, September 2026). Sample data in some registers may still be in German.
Ready for NIS2
See the NIS2 software, or first determine free of charge whether your organisation falls under NIS2.
Know where you stand first
NIS2 explained
National laws
The developer behind NIS2-Manager
Thorsten Schmitz-Hübsch is founder of TSMONDO UG and developed NIS2-Manager himself. As an external CISO and information security officer, he currently guides several organizations through their NIS2 implementation based on ISO 27001. The software originates from this hands-on experience and real client mandates.
Country pages: Netherlands and Belgium (Dutch) · Belgium (French) · Austria (German) · Germany · France